Phishing Report Plugins
Installation and Usage Guide
Purpose
With the help of extensions for e-mail client software provided by TUD-CERT, fraudulent and malicious E-Mails can be reported quickly and easily. This includes particularly so-called phishing e-mails, which are used by attackers to obtain critical information such as credentials and personal data. In addition, e-mails with potentially malicious attachments such as unknown executable files or malicious Office macros are also report-worthy. TUD-CERT analyzes incoming reports and takes countermeasures as necessary.
Phishing report plugins are currently available for the following E-Mail client software:
- Microsoft Outlook 2016, 2019, 2021 and 2024 (Windows); 2024 for Mac in Legacy Mode (macOS)
- Webmail portal of TU Dresden (Accessed via browser)
- Mozilla Thunderbird 115 and newer (Windows, macOS, Linux)
With these plugins, e-mails can be reported either as a phishing/fraud attempt or as spam. As a rule of thumb, e-mails from unknown senders that contain questionable, urgent calls to action (e.g., “Click here to unlock your account”) or suspicious links should be reported as phishing/fraud. Unwanted promotional e-mails, on the other hand, can be reported as spam and will be used by us to train the spam filter. Please do not report e-mails that have already been correctly identified by the spam filter and automatically sorted into the spam/junk folder.
Microsoft Outlook
Plugin activation
The reporting plugin is activated by default for all mailboxes at TU Dresden and is automatically downloaded when using Outlook. No separate installation is required.
Reporting suspicious e-mails
To report suspicious e-mails to TUD-CERT using Microsoft Outlook, select the e-mail in question and then click on the Report E-Mail button that appears on the far right of the ribbon:
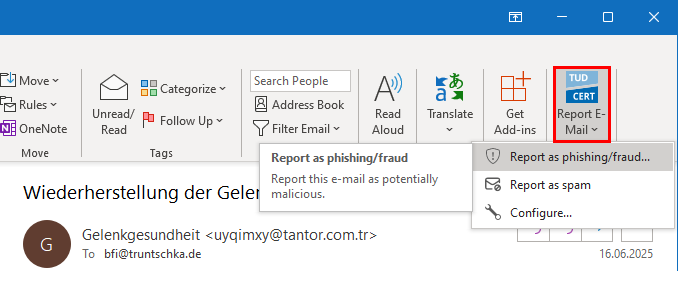
There are three options to choose from:
Report as phishing/fraud...: Select this option to report potentially malicious e-mails that you suspect to be fraudulent. You can also use this function if you are unsure about the legitimacy of an e-mail and would like feedback from TUD-CERT.Report as spam: E-mails reported with this option are classified internally as advertising/spam and used to train the spam filter. No further inquiry is made and the e-mail is automatically moved to your junk folder.Configure...: Allows you to adjust the behavior of the Add-In. In the current version, you can choose whether and to which folder e-mails reported as potentially malicious should be moved automatically after the report.
When using the Add-In for the first time, a prompt like the one shown below may appear:
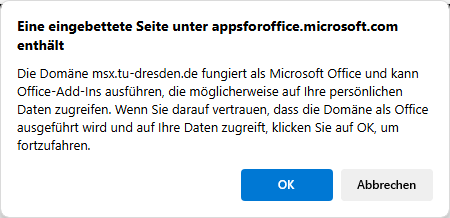
This is a notification from Outlook that the Add-In can access contents of your mailbox, which is essential for reporting e-mails. To be able to use the Add-In, you must confirm the request by clicking OK. It should not appear again afterwards.
If you report an e-mail as potentially malicious via the first option, a report form will appear in the sidebar. Here you can add an optional comment to the report, which will be visible to TUD-CERT employees:
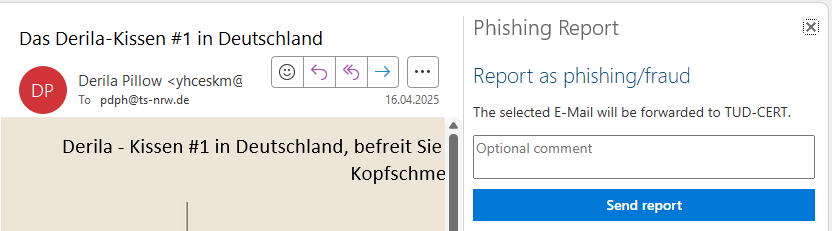
By clicking on Send report, an E-Mail is automatically sent to TUD-CERT in the background with your message, concluding the reporting process. If the report could not be sent successfully, first make sure that you have a working internet connection and then try again. If it is still not possible to send a message after several attempts, please send us an e-mail together with the error message to cert@tu-dresden.de.
By default, the reported E-Mail is also moved to your junk folder. If you want to change this behavior, open the Add-In menu again by clicking the Report E-Mail button and select Configure..., whereupon the following configuration dialog appears.
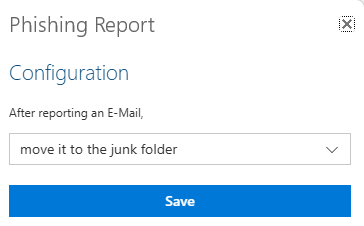
Reported e-mails can be moved to the junk folder, the recycle bin or not moved at all.
Disabling the plugin
To deactivate the Outlook plugin, follow the steps for deactivating the plugin in the webmail portal.
Webmail portal
Plugin activation
The reporting plugin is activated by default for all mailboxes at TU Dresden and is automatically downloaded when using the webmail portal. No separate installation is required.
Reporting suspicious e-mails
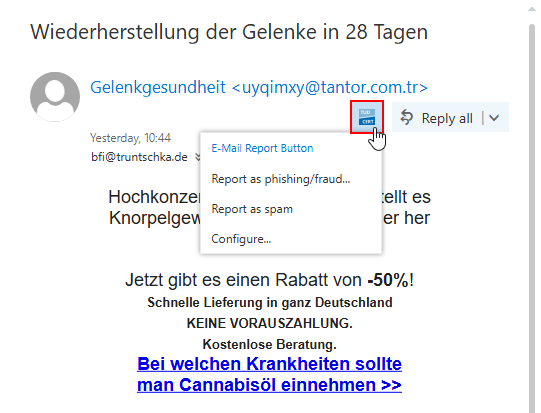
The reporting process in the TU Dresden webmail portal is similar to the reporting process via Outlook, the dialogs and forms are identical. Only the report button itself is in a different place. If you have opened an e-mail that you want to report, a small blue TUD-CERT logo will appear to the left of the Reply all button. If you click on it, the same menu as in Microsoft Outlook appears with the options already described above:
Disabling the plugin
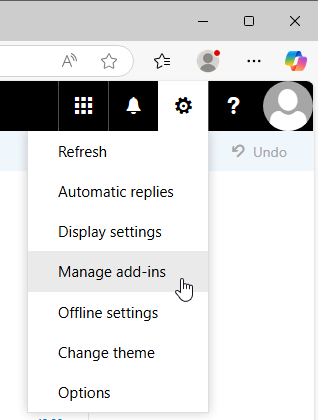
The reporting plugin for Outlook and the webmail portal can only be deactivated (or reactivated) via the TU Dresden webmail portal. Log in and click on Manage add-ins in the settings menu in the top right-hand corner of the browser window:
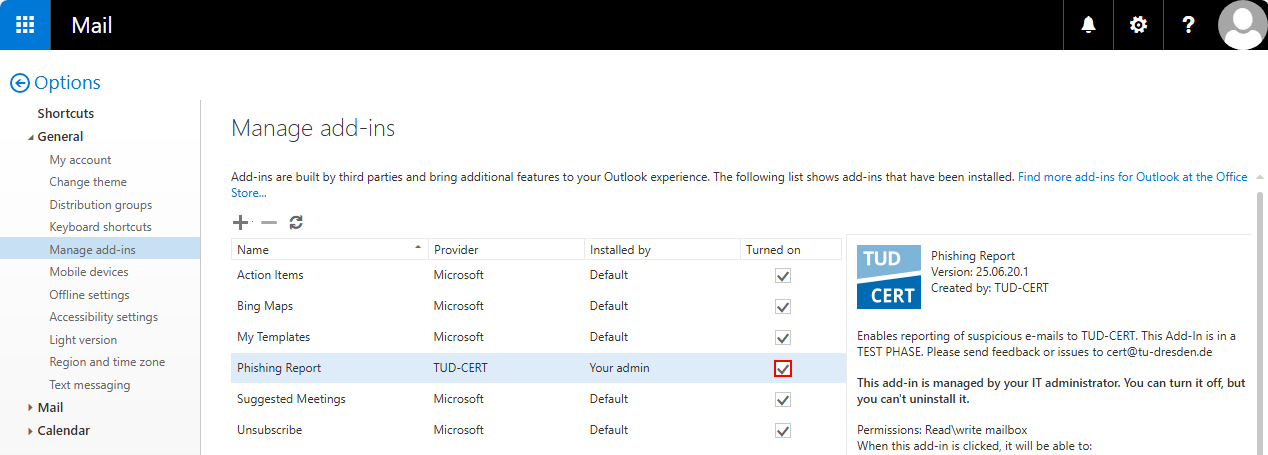
A list of available Add-Ins appears. Use the checkbox in the Turned on column of the Phishing Report add-in from the provider TUD-CERT to enable or disable the reporting plugin:
It may be necessary to restart Outlook to apply these changes.
Mozilla Thunderbird
Installation
The plugin for Mozilla Thunderbird requires at least Thunderbird version 115. For technical reasons, the latest version of the plugin is only compatible with Thunderbird 153 or later.
Note: Mozilla Thunderbird is released in two channels - either monthly or as an annual ESR (Extended Support Release) version, which receives updates over a longer period of time. Starting with version 153, our plugin is compatible with both variants.
The plugin is available for download from the official Mozilla Thunderbird Add-On website and can thus be installed directly from within Thunderbird on Windows, macOS and Linux. The following instructions show the installation process under Windows, but the steps under other operating systems are quite similar.
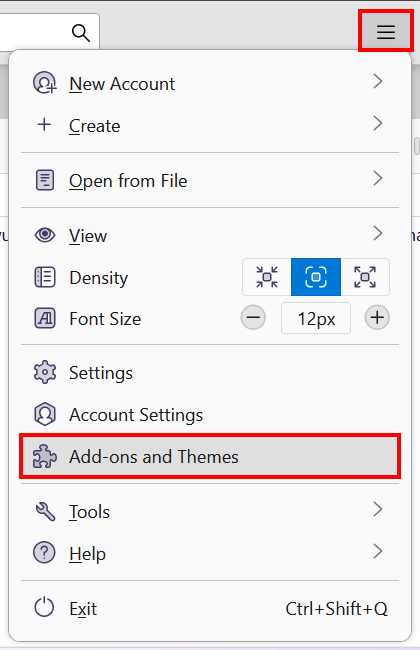
Start Mozilla Thunderbird, select the E-Mail tab and click the menu icon on the right edge of the window. In the menu, select the entry Add-ons and Themes:
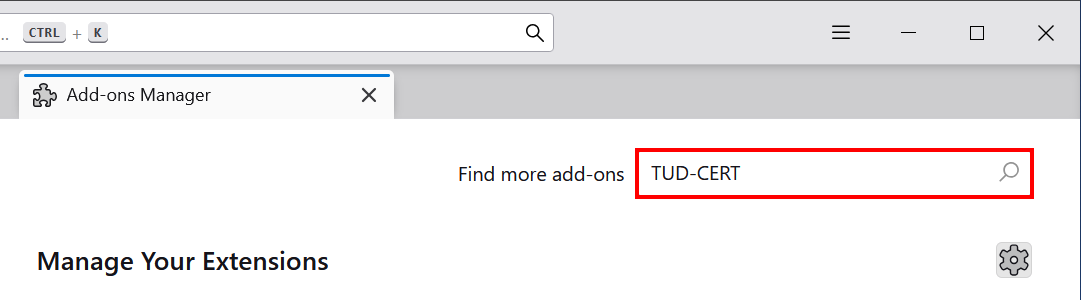
The tab Add-ons Manager will be shown. In the “Find more add-ons” field search for TUD-CERT and confirm the search request with the Enter key:
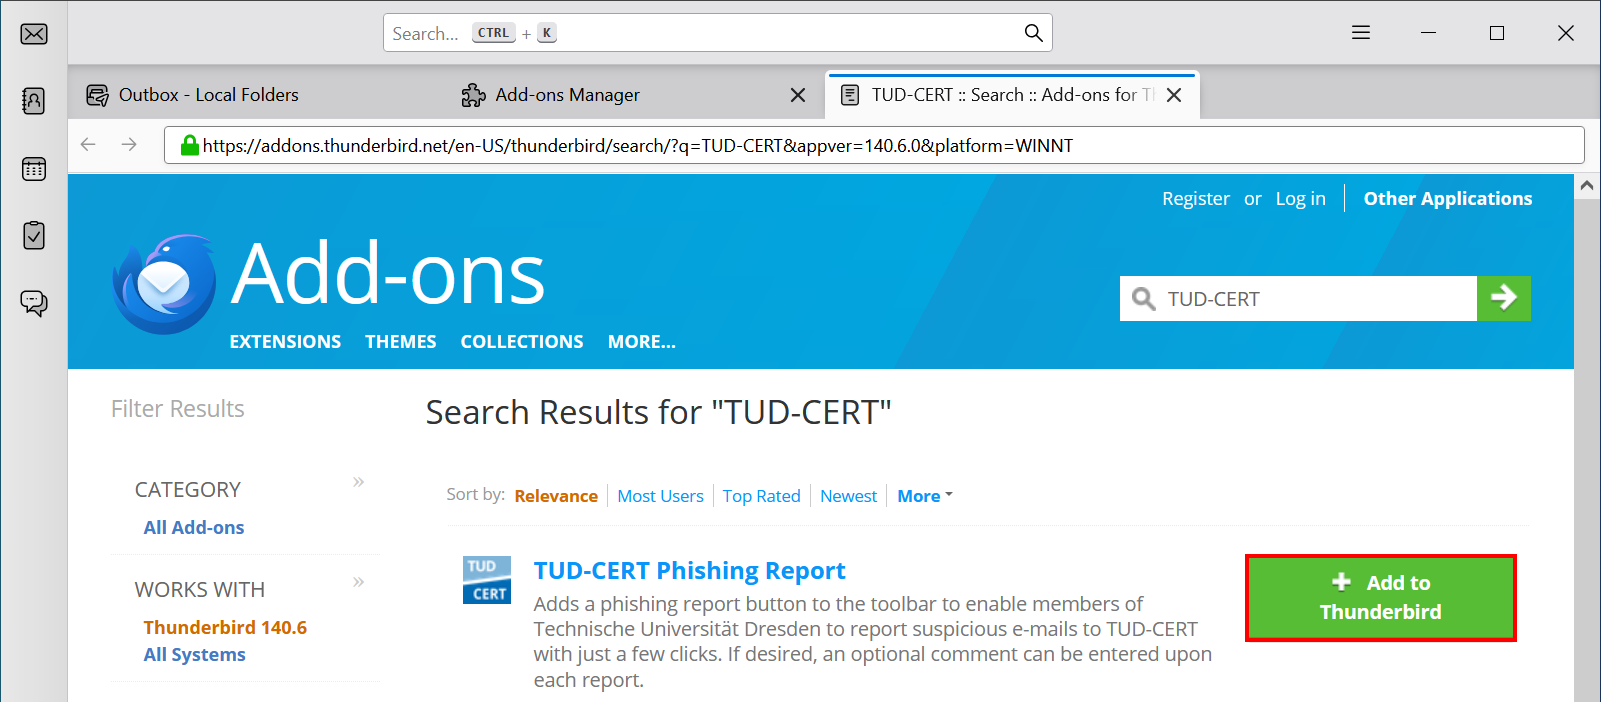
In the list of results, look for the plugin named TUD-CERT Phishing Report and click the button Add to Thunderbird.
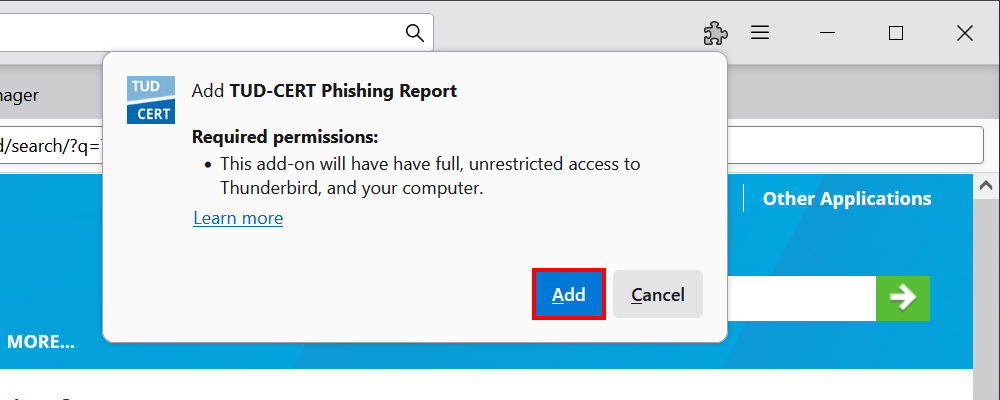
A dialog box lists the permissions required by the plugin and explicitly asks for permission to continue the installation. Confirm by clicking Add:
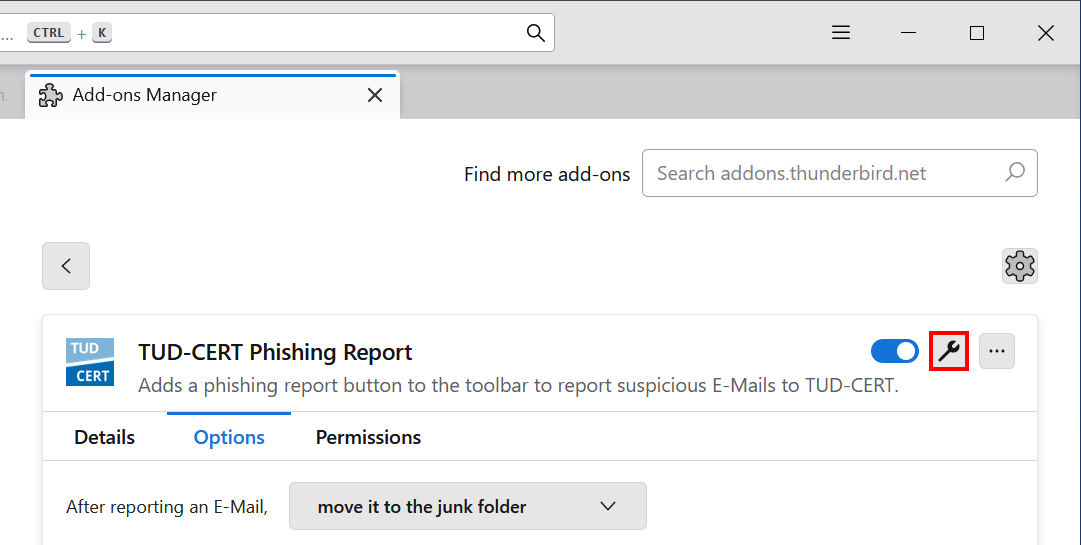
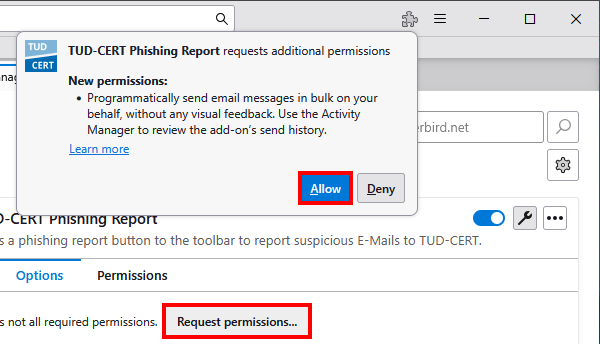
After a final dialog box was confirmed to complete the installation, the plugin is active and ready to use. In addition to the permissions already accepted during installation, the plugin also requires explicit permission to send e-mails as part of the reporting process. That can either be requested via the plugin settings, as shown below, or it will appear automatically when attempting to send the first report.
Optional: Some aspects of the plugin’s behavior can be adjusted to your needs. To do so, click the wrench icon next to the TUD-CERT Phishing Report plugin in the Add-ons management view, which will reveal the plugin settings. Here you can choose whether a reported fraudulent E-Mail should automatically be moved to the junk folder, the trash or - alternatively - be kept in its current folder. E-mails reported as spam will always be moved to the junk folder. If you made changes to these settings, confirm them with a click on the Save button.
You may also explicitly grant the remaining plugin permissions required to send e-mails:
Reporting suspicious E-Mails
To report suspicious E-Mails to TUD-CERT, view the E-Mail in question, then click the button labeled Report in the preview window of the E-Mail, as show in the following screenshot:
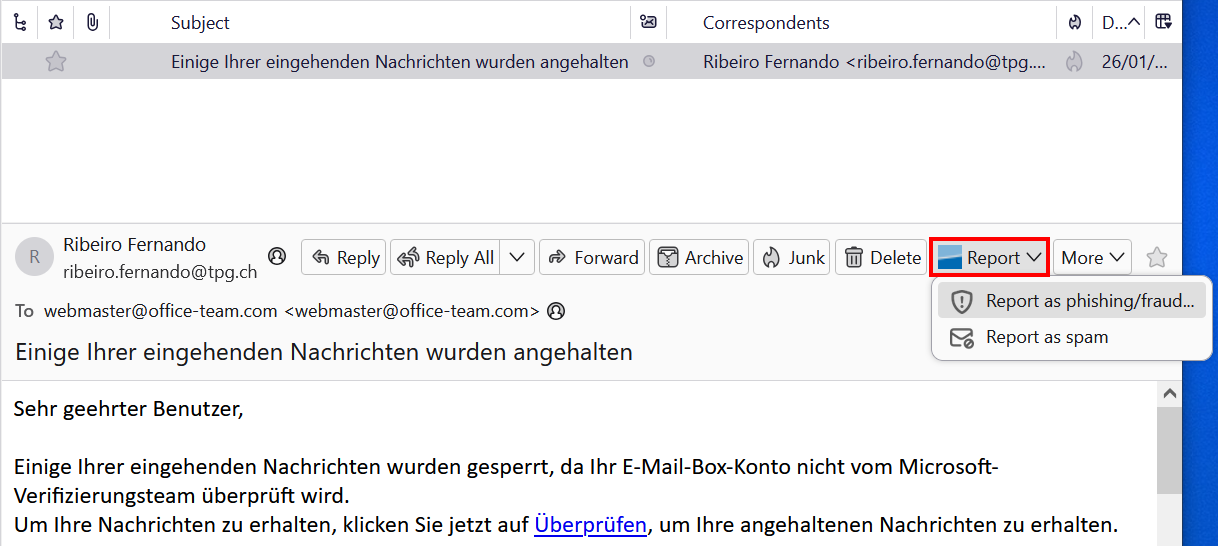
The following actions are available:
Report as phishing/fraud...: Select this option to report potentially malicious e-mails that you suspect to be fraudulent. You can also use this function if you are unsure about the legitimacy of an e-mail and would like feedback from TUD-CERT.Report as spam: E-mails reported with this option are classified internally as advertising/spam and used to train the spam filter. No further inquiry is made and the e-mail is automatically moved to your junk folder.
If you report an e-mail as potentially malicious via the first option, a report popup appears. Here you can add an optional comment to the report, which will be visible to TUD-CERT employees:
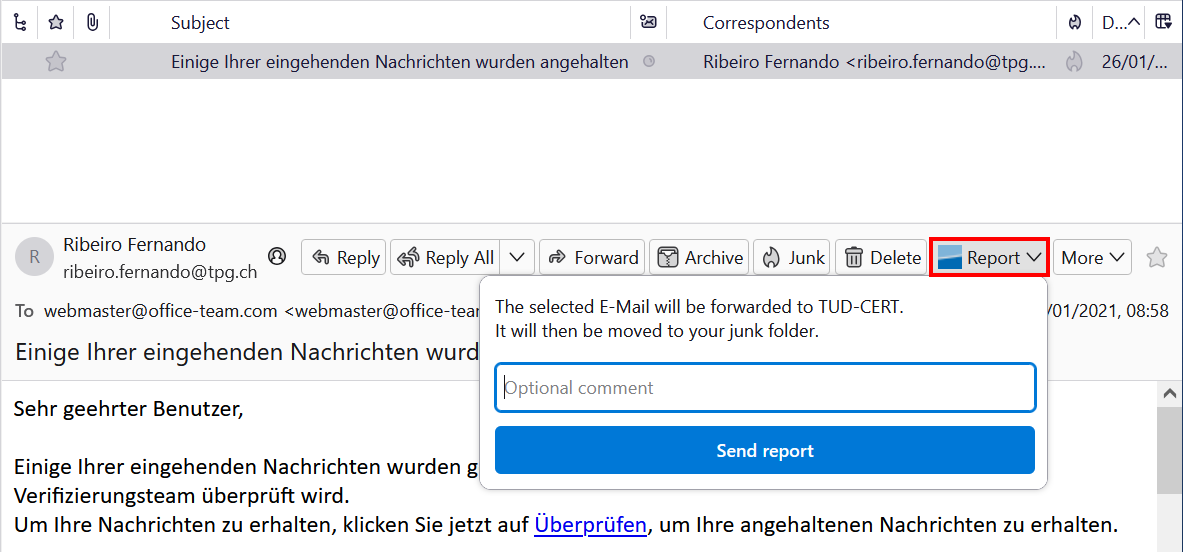
With a final click on the button Send report the selected E-Mail will be reported to the TUD-CERT, which may take a few seconds. If the message could not be sent successfully (an error message appears in the popup), first make sure that there is a working Internet connection and then try again. If reports fail even after multiple attempts, please notify us by sending an E-Mail to cert@tu-dresden.de.
FAQ
Why does the report Outlook Add-In button not appear even though the Add-In is activated?
Microsoft Outlook periodically asks the server for a list of activated Add-Ins, which is why it may take some time after the Add-In has been activated until it actually appears in the ribbon. Sometimes restarting Outlook helps, otherwise just be patient. Please also note that, for technical reasons, digitally signed or encrypted e-mails cannot be reported at all via the webmail portal and can only be reported with newer Outlook versions (see also the following entry).
Can digitally signed or encrypted e-mails be reported?
This depends on the used e-mail client. For technical reasons, it is not possible to report digitally signed or encrypted e-mails in the webmail portal or under Outlook 2016. Outlook 2021 and 2024, however, support the reporting of digitally signed e-mails.
I’m still using the legacy phishing reporting plugin for Outlook. Should I switch?
Our legacy phishing reporting plugin, which was only available for Office on Windows, is no longer being developed by its manufacturer. It will remain functional for the time being, but we recommend uninstalling it and using the plugin described on this website, which also works in the webmail portal as well as on macOS and works without installation.
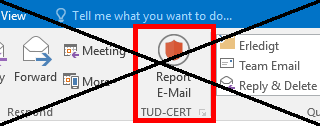
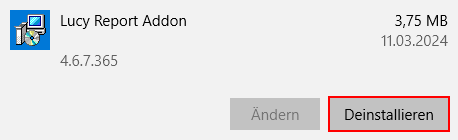
To uninstall the legacy Windows plugin, open the Apps and Features section in System Settings. The product is called Lucy Report Addon. Alternatively, contact your administrators.
Why are reported e-mails sometimes not moved immediately when using the webmail portal?
If you report e-mails with the Add-In from the webmail portal shortly after logging in (typically within the first 30 seconds), they do not appear to be moved correctly to the junk folder or the trash (depending on your configuration). This is an error in the webmail portal where the e-mail has actually already been moved server-side, but this state is shown incorrectly in the webmail portal. In this case, it helps to refresh the page once, e.g. by pressing the F5 key.
Where can I turn with feedback or problems?
Please send any questions, problems or suggestions for improvement via e-mail to cert@tu-dresden.de.